Cyber threat intelligence
Cyber Threat Intelligence
Clear, deep and dark web monitoring, threat-actor tracking, vulnerability intel and an attributed IOC firehose with analysts behind it.
- Sources
- 30B+ data points indexed
- Modules
- Foresyn - Tracer - Threat Advisory Suite
- Analysts
- DARKMON TIRU verifies the feed, writes every advisory and report
- Integration
- SIEM / SOAR / MISP via REST API and TAXII 2.1
The problem
You learn about threats after they land
SOCs are reactive; the adversary already operates with full visibility on your people, brand and infrastructure. By the time an alert fires, the campaign is already under way.
How DARKMON solves it
We work the adversary's side of the web
A Foresyn indicator opens the actor, Tracer follows it into your own data, and the Threat Advisory Suite tells your board what it means.
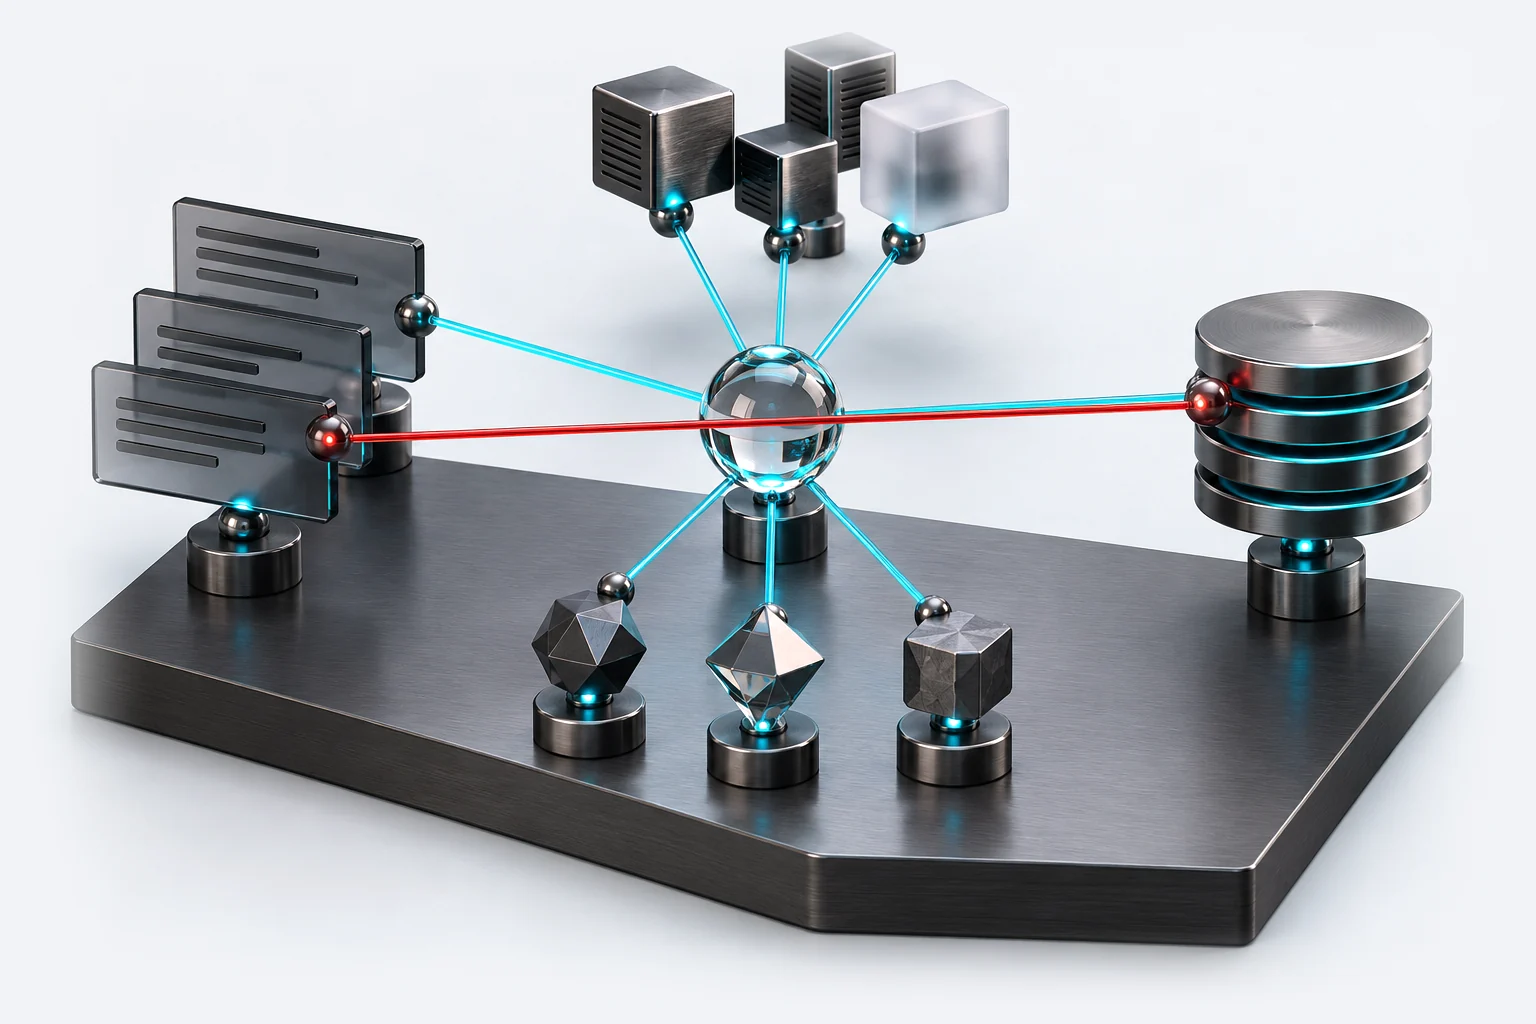
Real-time clear, deep and dark web monitoring
forums, Telegram, paste sites and breach sources.
Correlation and attribution to threat actors
with campaign tracking, and graph investigation in Tracer.
A continuous, attributed IOC firehose
served to SIEM / SOAR / MISP through the REST API and TAXII 2.1.
Vulnerability intelligence
CVSS plus real-world exploitability, zero-day feed.
Analyst context tuned to your sector
Threat Advisory Suite: advisories, flash advisories and tailored reports.
What solves this
Choose the product for your need
Three standalone products, licensed by use: Foresyn by API calls, Tracer by searches, the Suite by reports. Users and keys are unlimited.
- CTI
Foresyn
Threat IntelligenceThe intelligence engine continuous clear / deep / dark web coverage, threat-actor attribution, vulnerability intel and an IOC firehose over the REST API and TAXII 2.1. Generic, with no assets.
CoversIOCsThreat actors & malwareRansomware & DDoSVulnerabilities - CTI
Tracer
Threat Hunting PlatformOne search across your own asset data and DARKMON's collected intelligence, drawn as one link graph.
DeliversGraph investigationTracer Cases10,000 searches a year - CTI
Threat Advisory Suite
Analyst-led threat intelligenceDARKMON TIRU advisories, flash advisories, 12 tailored reports a year, hunts and briefings.
DeliversAdvisory libraryTailored reports and huntsRegional reporting and briefings
Get in touch
See what the adversary already knows
Review the intelligence against your environment and meet the analysts in a 30-day proof of concept with full feature access.